Tuesday, March 18, 2014

I'm up to here with Privacy!

Don't get me wrong, I like my Privacy! But everyone trying to legislate for it or protect it, are missing the slow creep of change. Security folks are even largely missing this change, though they might argue that they catch the real issue obliquely under the guise of the I or A in C.I.A. that is Integrity or Availability

But sadly Integrity or Availabilty do not cut it...

It's about Control, or more correctly the downside, ie "Loss of Control". Take a look at the real threat behind Advance Persistent Threats (APTs).  Many of the famous one's had no interest in exfiltrating information, that is threatening Confidentiality or Loss of Privacy. They were about taking control of the assets they were attacking whether alternating rotational speed of centrifuges, in order to cause them to self destruct. or just prior to the attack on Iraq taking control of the Iraqi military Communications, Command & Control system. 

In short Agency is the thing we should be maintaining and protecting not Confidentiality or Privacy. Basically because if the right entities are "In Control" of the right assets then most security problems are solved. 

In order to keep control in the right hands, our focus should be on Identity, and Entitlement.
Watch the Jericho Forum Identity, Entitlement, and Access Management videos on YouTube.

Some call Entitlement; Rights Management, sadly this term has been discredited due mainly to the fact that initial "rights management" implementations were used by the music industry to reduce or control the rights of listeners asymmetrically, i.e. in a manner that is similar to the "Heads I Win, Tails You Lose" model of control.

Effective controls have to be symetrical, with the right entity being in control of the right assets, in order for this to occur, legislators should stop focussing on Privacy, and start focussing on Agency.

We are living in a world where Agency is being, at best reduced, at worst destroyed. Devices are being built and sold that Never give full control to their users. The early PC was Agency neutral, it arrived with no one in control, the owner could gain "Root" access to the device and take full control. more recently devices arrive that can never be controlled by the owner of the device. Sony took control of their Play Stations away from their owners, Apple never gave iPhone Users control, they tried to keep it, "JailBreaking" being the only means of gaining "Root" access.

Samsung Smart TVs are another example of a class of devices that denies control to their owners.
I blogged on this earlier.

Imagine, if you will a world where devices like for example an aeroplane could be configured to act in a manner not directed by the pilot or co-pilot. The current conundrum of the missing Malaysian Airline could well be explained by catastrophic loss of Agency. The communications, command and control systems on the plane are all controlled by software normally controlled by those in the cockpit.  A malicious third party, or nation state may have inserted an APT that took control of the plane. Was this a trial run of a new form of terrorism? 


Agency is far more important than Privacy. We need to focus on keeping control in the right hands.

It may turn out to be a pilots malicious actions, either way it is an Agency problem!

"He says typing on an iPad that he doesn't have full control of!"

(As I have stated before the word Agency is not being used in it's more recent organisational construct.)

Tuesday, February 25, 2014

Aargh! Yet another Raised Bed/Silo in my Walled Gardens

The Internet of Things will hold far less promise if everyone follows the Hive path that British Gas have chosen.

For those that do not know "Hive" is a means of controlling your home heating, and hot water if you have an old fashioned water tank! It comes with a very nifty and useable App, and it can be controlled via the HiveHome website. A word of warning don't forget that you are in Demo mode, I can vouch for the fact that it is very annoying to find you have programmed your whole system in Demo Mode!

The Bottom Line...
British Gas have apparently licensed the AlertMe hub, but taken the Zigbee protocol and made it their own (ie Proprietary Protocol!)

Grrr,  my Home Automation Agency is already under attack! I started looking up "Hive API" as soon as it was installed, by a very kind British Gas engineer named Josh who explained that I could get it done for £179, as he was already here servicing the boiler. I was hooked. I failed to do my normal due diligence!

No APIs currently available or planned. (Though they have been hinted at) :-(
I checked IfThenThat.... nope Hive is not present? :-(

Apparently I can use SMS as an API interface, thanks for that British Gas!

So now to follow my own advice, after the fact, what data/control have I just given up, and can I get it back?

Watch this space... I am still pondering that question. 

We are likely to see many more examples of Walled "Internet of Thing"s Gardens
In fact my Internet of Things garden is starting took like my own garden, a hodge pudge of poorly connected raised beds, think silos of things. 

The X10 System 
The Withings Scales
The Weather Station
The Blood Pressure Monitor
The Heart Rate Monitor
The Mac based Indigo Home Automation System
The Hive
The Solar Panels
The OWL Electricity usage Monitor
The Electric-Save Electricity usage monitor (Don't ask!)
The X10 Secure Alarm System
The Phillips Multifunction Remote
The Apple TV
The TiVo
The PS3
The Samsung Smart TV
The Airport Expresses (iTunes)

My iPad Mini with
   Withings App
   Hive App
   Apple Remote
   Indigo X10 App

No prizes for guessing that they are NOT fully integrated! Yes all of them can connect to the Internet!

I want my IoT Agency to be simple to manage and easy to integrate!

Some Hope!

Dear British Gas,
 You do not understand the power of co-creation. You have treated me just like the crab in my prior blog post. Please reconsider your stance!

Adrian


PS I am off to read the Terms and Conditions, I really was badly hooked !!

Dear Satya

I am looking for a cyber knight, some one who will bring "Human Agency" to the internet and protect it. By Human Agency I mean the capacity to control one's environment, when the environment is the internet, it might be called Cyber Agency.

To give an Entity (Government, Organisation, Person or Device) Agency, there are three things that must be sorted:-
1) The ability and capacity to trust the identity of remote entities,
     whether Anonymous (but same) or Named (and verified)
2) The means to transact in a trusted manner, ie negotiate, contract, commit, deliver, and pay in whatever persona we chose.
3) The opportunity to collaborate in a trusted environment

For me the current manner of attempting to achieve this with secrecy is doomed to failure.

We need an open trustworthy ecosystem, to accomplish the above.

I believe Microsoft can be one of the reasons that this ecosystem can come into being.

Please help us move from the "Agency Free" Enterprise/Network space through the "Agency Impaired"(App/Service)^2 domain to the "Agency Enabling" Entity/Device/Data Nirvannah


Is it just me?

I get the sense that we are sleep walking into a world devoid of human agency, a world where the machines are talking to machines, and corporations are taking the profits.

Human Agency defined previously here; is something that we innately desire, but are too often giving up in exchange for mere fripperies. A free game gets access to our location, our friends, and all their details and even the right to change our address books, without any further input from us, and often with not even a tiny shiver of fear.

Many moons ago I was advised to cook a crab by placing it in cold salt water and slowly bringing the temperature up, as it would not notice before it was too late, that it was in "hot water".

The water is getting warmer, and yet we still do nothing but click on anything that gives us "something for nothing". Except, it is our "Agency", it is not nothing! If we give it away it will be very hard to get back. Atfer all the web never forgets...

If Religion is the opiate of the People, then Apps are the Designer Drugs, and Devices are the Syringes!

Inject them into your life at your peril!

At least think before you click...
"What am I giving away control of, and why, and can I get it back?"

Remember: We are the Crabs!

(With thanks to the Orrinjohnson.com blog)

Organisations that understand these issues will be empowering us to be in control of our cyber selves, there will be a new breed of corporations that understand that e-trust is something hard to acquire and easy to lose. Which is the best type of Competitive Advantage there is! 

As the Internet of Things takes off, there are likely to be two sorts of organisations, those that seek to lock us in, and make us the product, and those that seek to "Co-Create" with us and make us their loyal partners and customers.

What to do...

Enterprises should ask:
How to invest in a Collaborative Future?
How to avoid cooking your customers? 
How to compete in ways that develop Human Agency?

Governments should ask:
How to legislate to protect Human Agency?
How to achieve compliance?
How to punish the theft of Human Agency?
How to empower the populace? (Education?)

Individuals should ask:
How can we (Co-)create our future?
How do we get out of the pot?
How to support organisations that protect our agency?

For the machines might get to ask; "What benefit do these fleshy things bring to our world?"

Deep down it is about Trust and Values, ours and theirs,
and the ecosystem that will support Human Agency.

Some might call this Freedom, which is surely worth fighting for!


Monday, February 03, 2014

The Missing Commandment

Having been intimately involved in the development of the original Jericho Forum Commandments, https://collaboration.opengroup.org/jericho/commandments_v1.2.pdf there were a lot of hours spent in many fuggy rooms, with drained coffee flasks more often than not, with some very impressive individuals.  It is only now many years afterwards that I realise that we missed a key commandment, arguably the most critical of the commandments.  

Happily there are a number of precedents, for missing a keystone Commandment, the fundamental principle, the prime rule, or key law.  Jesus in John 15:12 did this when he gave us an additional commandment, "Love they neighbour as I have loved you", presumably because he recognised that the original commandment covering this area, relied on human foibles; "Love thy neighbour as you love yourself."

My favourite example of realising a "law" was missing and adding the missing law was achieved by Isaac Asimov after his Three Laws of Robotics:

"1. A robot may not injure a human being or, through inaction, allow a human being to come to harm.
2. A robot must obey the orders given to it by human beings, except where such orders would conflict with the First Law.
3. A robot must protect its own existence as long as such protection does not conflict with the First or Second Law."

After Asimov started to have robots, like Daneel, have impact on humanity, he recognised the need for a Zeroth Law:

"0. A robot may not harm humanity, or, by inaction, allow humanity to come to harm."

Some apparently establish the prime law in their initial attempt, in 2009, Robin Murphy (Texas A&M) and David D. Woods (Ohio State) proposed "The Three Laws of Responsible Robotics" 

The laws are as follows:

  1. A human may not deploy a robot without the human-robot work system meeting the highest legal and professional standards of safety and ethics.
  2. A robot must respond to humans as appropriate for their roles.
  3. A robot must be endowed with sufficient situated autonomy to protect its own existence as long as such protection provides smooth transfer of control which does not conflict with the First and Second Laws.
I suspect that even this set of laws could be manipulated in true Asimov style to posit the need for a Zeroth Law "A Robot may not deploy a robot without embedding these laws within it."

However I digress, and am in danger of starting to explore the areas of ethics and trust, so back to the missing Jericho Forum Commandment. When we created the original 10 Commandments we added an Eleventh to ensure that Secure was the Default position.  At the time we coined the Deperimeterization word, it was clear that we had information security at the fore front of our thinking.   (I got over the 's' vs 'z' spelling tension after I learned that 'z' was originally used in Olde English.) We saw the term had two fundamental meanings, the first to imply that it was a natural entropic force that impacts all information, resulting in reduced integrity and data spread.  The second to imply the existance of a set of external negative forces attacking the structure and value of the data.  Both of these meanings could arguably be covered with what I have recently identified as Anti-Clockwise Security. (Shorthand for having a largely Information Risk Reduction mindset)

The 11 Commandments were split into 5 areas:
  1. Fundamentals
  2. Surviving in a Hostile World
  3. The Need to Trust
  4. Identity, Management, and Federation
  5. Access to Data

So what is the missing Commandment?

The fifth area; "Access to Data", arguably signals that we were discussing the underlying concept of the Zeroth Law in those fuggy rooms.  I posit the Zeroth Law should cover the basic concept that data should not be stored, by interested parties; rather, the relevant information should be accessed.  As an example; an entity should not need to transfer their precise date and time of birth, arguably a critical identifier, to a third party who simply wants to know that they are over 18.  Another example would have the reader, listener, viewer or player being trained to understand that they are no longer acquiring full rights to a physical asset, but they are being given licensed access to digital assets, the two books that I just connected to my Kindle account are such examples.  We are in a transitional era moving from physical to digital, paper to silicon, silo to network, moving from egosystem to ecosystem.

In this transitional era, we are in an age of the "big data grab", whole industries are seeing it as their right to insert themselves into our data streams and hoover up all our data.  See my Samsung & LG TV blog posts.  In the prior "Physical" era we had got used to being able to "own" the intellectual assets of others, and felt we had the right to share the physical instantiation of their efforts, either an Vinyl LP or a Book, with others as we saw fit.  The creation of the Philips Cassette, and latterly Video Casettes even allowed us to make physical copies of such intellectual property, while it was being broadcast by radio and TV.  The artists or authors involved thus lost control over their assets in the physical era, and are still doing so in the transitional era.  Apple with it's iBeacon technology are rolling out a technology that has been architected not to share vast mounts of data, but arguably could be part of a huge hoovering effort, or the start of rolling out the solution, something to keep an eye on!.  As individuals we would do well to consider our digital address books, do we own the rights to all the data in our digital address book?  To this day, I still feel guilty about allowing Plaxo a look at my address book, apologies to any impacted by my faux pas! Hopefully no more than an increase in Spam!

As I have previously stated we need to shift from a privacy focus to an agency focus.  In order to achieve that shift and maintain control over our assets we need a new approach, a new mindset, a prime commandment?

"Owning entities should not allow their data to be uncontrollably stored by others"

Remember In the Jericho Forum we included the following as entities:
    People, Organisations, Devices, Code, and Agents.
We recognised that Agents were a special form of Entity that could be any of the five!

In the address book example implementing such a prime commandment would have the benefit of my address book always being up/to date, and not containing the addresses of folks who no longer want a Christmas card from me! Exploring the other examples I can only see positives, of course we won't be able abuse the assets of others, but surely that would be a good thing?

Oh yes the e-Trust ecosystem that enables this Prime Commandment is yet to be built, so until then consider carefully who you chose to give your data to.

To be clear the above is not the final wording of the Zeroth Commandment, simply my first crack at it...

Improvements welcome.

Aside: Before the Jericho Forum quiesced, we posited the need for a set of Jericho Forum Data Commandments, this would surely be one of the first of these?


Tuesday, January 14, 2014

So what drives e-trust in an Outside-In world

I started considering this question while fighting a cough that kept me awake until one am this morning.

We probably first need to define Outside-In and e-Trust:
The first definition will be the most difficult to capture in a single sentence, especially as LEF's own understanding of the concept is fast evolving, from being just an IT based paradigm focussed on platform location, to taking a more holistic business perspective resulting in the importance considering and engaging in the development of new business ecosystems, often powered by the fast evolving internet.

Outside-In
The approach or mindset of an enterprise or entity that makes use of an external network of partners and/or co-creators to expand the size of the network for the benefit of it's participants. This will more often involve the effective use of information or innovation sourced from the external network, than it will internally created information or innovation.

e-Trust
Involves the capacity to develop confidence during specific interactions, that involve specific assets, through various devices and systems across networks to other knowable and unknowable entities. One might call it Virtual Trust.

After my coughing bout, and a period of what felt like insane clarity, I fell asleep after having created the following seven top Level "A"s, as perceived by the end user.
(NB I did not concern myself with the deeper,  more technical components that will be required to deliver on these high level drivers.)

Affordance, Accessibility, Availability, Accuracy, and Agency....

I swear I came up with a sixth and seventh A, but as I fell asleep soon after with a deep sense of satisfaction, I failed to properly store it in my sleepy neurons.  Wait, they have appeared, I can't believe I momentarily forgot them, they are of course;

Authenticity and Authority

As I went to sleep, I gave myself the challenge of comparing these seven terms with the Parkerian Hexad, but first lets quickly define these seven drivers, not in any specific order. I will tweak the Wikipedia definitions to match the needs of this blog post. Remember we are considering the drivers of e-trust in an Outside-In world. I will not argue for or against these terms, I will just try and define them in the context of Outside-In.

Affordance 
The capacity of an object, service, ecosystem, or environment, to allow an entity to perform an action.
This term relates also to such concepts as usability, simplicity

Accessibility is the degree to which information, products, devices, services, or environments are available to as many entities as possible.

Availability is the probability that an item will operate satisfactorily, or information would usable at a given point in time when used under stated conditions in an ideal support environment. Simply put, availability is the proportion of time a system is in a functioning condition.

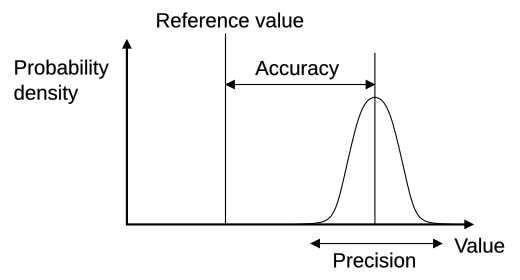
Accuracy The nearness or closeness of information to the actual value of information being accessed.

Agency is the capacity of an agent (a person or other entity) to act in a world, including controlling access to their own information.

Authenticity The genuineness of content or identity, actually possessing the alleged or apparent attribute or character,

Authority Represents the legitimacy of an entity to define formal rules or rights, established in law or by decree of the owning entity.

So onto my Parkerian Hexad comparison...

My seven terms Affordance, Accessibility, Availability, Accuracy, Agency, Authenticity and Authority

The terms from the Parkerian Hexad
  • Confidentiality
  • Possession or Control
  • Integrity
  • Authenticity
  • Availability
  • Utility
Two direct matches, but the rest all align to one degree or another


I believe that the seven more effectively represent the drivers of trust, rather than outcomes that influence the trust.


All this, apart from the last comparison, in a weirdly clear glimpse just as I fell asleep. It just felt right.

In the cold light of days I am starting to challenge the logic... what say you?

#40 To no one will we sell, to no one deny or delay right or justice.

Article 40 of the Magna Carta (1215) embodies in one sentence the concept of Agency.

#40 To no one will we sell, to no one deny or delay right or justice.


I was listening to a radio news article on the troubles besetting Egypt, when “agency" reared its head again…. For me having "agency" involves not having my rights, sold, delayed or denied.

The binary agency/control option is quite apparently the issue, with the Egyptian voters being given a fools choice.

Option 1) No i.e. you want the Prior Constitution which established the Muslim Brotherhood as the only option leading to a Police State
Option 2) Yes to the New Military Constitution which establishes the Military as the only option leading to a Police State

Getting the "Balance of Agency" right is never easy, I can’t see any easy way out, while neither side wants to truly create a pluralist society. I would commend those developing a new Egyptian Constitution to take the best parts of the Magna Carta.

The same goes for the Internet...

Option 1) Enterprise Centric  …. leads to exploitation of consumers data, and thus the consumers
Option 2) Network Centric …. leads to exploitation of consumers data, and thus the consumers
Option 3) Service Centric …. leads to exploitation of consumers data, and thus the consumers
Option 4) Device Centric …. leads to exploitation of consumers data, and thus the consumers

While Option 2) Network Centric Is currently dominant
(I hold the News Corporations to be part of the Network Centric Option, along with Broadcasters and Network Providers, in my mind Network is not just the wires.)
We are currently in a battle, perhaps as yet unrecognised, between the Service and Device Options for dominance. Clearly the Network Players will continue to fight to maintain their valuable, to them, dominance. Sadly it appears that all the potential winners want to sell, delay, or deny our data rights.

Put more starkly: Who will rule us, through our data, Google or Samsung?

(Apple is still straddling the fence between the two options but by targeting only the wealthier, they will likely be also rans.)
Amazon might be the white knight, if they help build an agency enabling ecosystem that gets the balance right. At present they are seemingly fighting for dominance in option 3, but they are not averse to fence sitting, with devices sold at a loss, if it helps them achieve dominance.

I don’t really like any of the above numbered options; where are the options that allow for the balance of control between providers and consumers. I am not looking for a compromise(d) option, I am asking is there a "Fourth Way"?

Do we need an Internet Magna Carta that focuses not on an individuals right to Privacy, but more on the right of entities and Society to control how their data are used. A charter that does not allow the selling, delay or denial of our data rights.

The intriguing thought I have is that the e-trust ecosystem designed to deliver on the needs defined in an as yet unwritten Internet Magna Carta, might be used to solve the wider societal difficulties that we face; as factions, formed from religion, tribe or dogma continue to rip our plant apart. Only this week we had a world leader get embroiled in an affair of the heart which interfered with the affairs of his state. We also had an individual chose to eat the raw limb of an opponent he had slaughtered as retribution for the loss of his own family members, we are living in a crazy world.

Clearly criminals would not be allowed to hide evidence of their crimes, nor Leaders hide their true values, but isn't it reasonable for us to want entities to have balanced agency?

Let’s build an e-trust eco-system that helps hold our leaders accountable, and achieve an agency balance that; supports rights of many different factions, encourages the growth of enterprises with the right values, ensures the continuation of a trustworthy global communications network, helps reward the development of valuable services, and creates a demand for devices that are valued.  We might call this Internet (or Social Media) enabled phenomena Social Capitalism! Either way “Agency" in the new system should be balanced in favour of no ONE entity or organisation.

Intel has written a paper on the upcoming Data Society in which they wrote "Today, we do not control most of our personal information. People in the future may "want to have more transparency and control over the use of their data." and perhaps more importantly: "We don’t know enough about our own data, and its value."

I hope that this new option will be “Value(s) Centric"

With an e-trust ecosystem in place perhaps we could build a Pluralist Outside-In Society?

I believe that this would be as valuable for the enterprises currently being marginalised in the batlle for dominance as will be to the consumers who are being increasingly exploited.

Whether Extremist Christians or Extremist Muslims would be happy to live in such a society is another matter.

Sunday, January 05, 2014

The big reveal!

I don't know my left from my right! You would however never know as I have a memory implant that gives me the answer on demand. While you can see the implant if you look carefully, you can't see when or if I operate it. A nasty collision with a wooden post in the early 60's, gave an RAF orthodontic surgeon, the excuse to experiment with this futuristic device.

To my delight I mastered the implant with ease, and have been using it ever since. It has no batteries, and has only had to be serviced twice in 50 years, once when the original materials decayed, and once when it came unstuck.

The reader is my tongue, the implant is simply a cap on what remains of my left incisor.

What the heck has this got to do with e-trust I hear you cry! Well actually far more than you might think. 
Having perused the recent news that Google is looking to allow you to unlock Chrome without a password, by using your mobile device, but were concerned that the devices might be abused, my surreptitious tongue interface came to mind. 

If I could give my tooth the power to communicate with my device, I could allow Chrome to automagically authenticate me through my device and then confirm my authorisation with a secret tap on my tooth.

An extension of the now hopefully not patentable idea, as I have put it into the public domain, is to piggy back an interface onto the nerves controlling the muscles in a particular area of ones body. then the user the would teach their identity agent their particular secret musculature confirm command.

For the challenge with establishing if any authentication signal was correct is first establishing with a high degree of authority the actual intent of the principal in question. There would also need to have a secret duress signal. Even more capable identity agents would have the capacity to detect the amount of blood in my alcohol! Authorisation would ever be allowed when it was high enough!

Too often are actions taken to be meant, this is not always the case.

Accepting actions without intent is a very fast way of denying the agency of the principal.

So when will I be able to get my dentist implanting my dental authentication device?
Perhaps more importantly what will it be called? 
Yorkshire Version = t'authorise
Modified Joke  = 2or30 ( two authority ok a stretch but close in an Irish accent)

Or a strap round my ankle that detects me twitching my left big toe, three times.
"Trust Ankor"?

It is not sufficient for a device to be able authenticate my ident, my device will need to confirm my intent, the two are very different problems.

As we shift to an Intention based economy this will be a real issue, for which we will need answers.

Thursday, January 02, 2014

Avoid Abrogation and/or Disintermediation on the journey to Outside-In

Two of the most dangerous aspects of the Outside-In journey are Abrogation and Disintermediation. So how do these two concepts relate to Outside-In?

Firstly, it is important to understand that the Outside-In frame, identified by the Leading Edge Forum, is an important new business trend, the antonym of Inside-Out, that results from the confluence of social connectedness and consumerized devices, that are empowering customers and partners. Organisations that understand this trend and are starting to explore its implications, and learning to live with the new frame, should become aware of the new opportunities, as well as the barriers and risks that the confluence also brings. Remember often the best data is "out-there", not inside your own organisation.


Abrogation is the result of choosing to allow rights over, or access to key data and / or business processes to be transferred to external entities or simply let go. This is very different than the act of choosing to make such data publicly available. Once an organisation has abrogated their rights over such data or business processes, it is very difficult to regain those rights.


Disintermediation has a similar result, ie the loss of rights over or access to key data or business processes, but in this case through the deliberate acts of external entities to gain control over those rights.

It is important to remember that much of the key data used to run an organisation profitably are actually owned by external entities, either partners or customers.

It is critical that Outside-In business processes are architected to allow the control over such data to be in the hands of the most appropriate entities, while maintaining access to such data.

This is arguably a security question, though clearly it is a question that involves collaboration and  co-operation with partners and customers. As identified by the Jericho Forum the future is "Collaboraion Oriented", and so we need Architectures that are also collaboration oriented.

Given we recognise that most current business architectures were developed for an Inside-Out frame .

Are the architectures your architects are developing focussed on the Inside-Out or Outside-In?

Do your architects have the skills and knowledge to develop architectures that enable your organisation in an Outside-In world?


Saturday, December 21, 2013

In Defence of the word Persona

There is currently an argument occurring in the basement of the internet, far away from the ears and eyes of the users of the internet, it is discouraging the use of the word Persona. There are some very good historic reasons for this position. It is indeed important to ensure that there is a very good reason to create new words or new meanings for old words.  Change should always be very well justified.

My position is that we need a word that describes the result of a user / entity compartmentalizing components of their identity. The result is an identity but it is not the full or complete identity of the entity in question; it is a partial identity selected for many reasons including context, risk mitigation, privacy, reputation management, and indeed avoiding boring a circle of friends who have absolutely no interest in my composting exploits..

The word I would use is indeed Persona. I would make clear that the word normally describes the result of an entity having agency over their identity. The number of persona(s)/(e) (or whatever the plural of persona is) and their scope would most often be in the control of the entity. There are however examples of persona that are not fully in the control of the entity, examples such as the Doctor persona, in the UK the BMA has a degree of control over such a persona. Convicted criminals rightly have less control over their Convicted Criminal Persona, and Prisoner Persona than they might wish for, with convicted paedophiles having even less control.

Agency over a persona is an important consideration, I read recently the term "owned audience" in the context of a marketeers view of web-site users. As an audience member I resent the idea of being owned. Sadly Marketeers tend to use the word Persona as something that they can apply to an entity, rather than a view of their identity that the entity chooses to use. This Forbes article from March exemplifies this unfortunate perspective.  Getting the appropriate balance of the control over persona will be an important shift in the future. Many device manufacturers see us as commodities that they own, rather than individuals with rights over our "TV Viewer Persona" for example, they are creating devices that can assume control over the attributes of our Viewer Persona. Both Samsung and LG have demonstrated this approach, with LG going as far as creating a control that it actually ignored, and worse collecting Filenames from connected network devices.

So here's to the word Persona, and a growing understanding of the personal nature and value of a persona, and the importance of having agency over our Personae, where appropriate. In the Intention Economy this perspective will be key!


Tuesday, December 10, 2013

On the wisdom of young wizards!

Let it be known that not all young Wizards are as wise as Harry Potter. In addition, even Harry made a few faux-pas as he struggled to come to grips with his newly discovered powers. The trouble with IT professionals, though sometimes that last word has a hollow ring to it, is they don't fully comprehend that they are still young wizards, and worse they seem to have managed to persuade a gullible set out "business people" that they are highly proficient. I listened to Radio 4 this morning hearing non IT professionals defend the "impairment" of £40 million, based on the fact that it is quite normal, in the IT industry, for vast amounts of useless code to be written, and then "written-off", or as Glenda Jackson so eloquently translated for us... "So, does impairment mean poured down the drain?"

The fault lies in the assumption that if someone can put two Lego bricks together then the next question can be asked "Why can't they build a full size working model of the space shuttle?". The answer is quite simple they are not quire ready for that Spell yet, for they have yet to master a myriad of spells which would make the building of anything that uses more than 50 bricks quite beyond their reach. Excuse the mixed metaphors but as anyone who has tried to build the moving staircases of Hogwarts out of Lego knows, it's not quite as easy as you might think!

Sadly, most wizard schools, only teach the young wizards how to connect a few bricks together! 


Sunday, October 27, 2013

On Magical User Interfaces

I had the pleasure of meeting Josh Blake last week on the LEF Study Tour, those that know him, will know that my mind is now filled with the wonders of Natural User Interfaces or NUIs

Natural... Hmmm .... of Nature
So they must at least appear Natural... which would mean that they would appear to be unsupported by technology.

I reach to Clarke's Third Law:
    Any sufficiently advanced technology is indistinguishable from magic.

So actually we are really after building MUIs!

Over the week we started exploring the various dimensions of NUIs
On the plane home I extended our list and mapped some of the relationships. I so needed Josh's patient thinking support
(Josh: I really did appreciate your gentle patience as you lowered me into this new space.... but I still have problems with your definition of NUI :-) )

So here in no particular order ( he says lying through his teeth)  are my latest dimensions:
Agency (OK so you knew I'd put that one first! For it's surely the "raison d'être" of any interface!)
Affordability (ie Affordance - look it up it does't relate to monetary cost, it's more like learning cost)
Efficacy = Affordability / Effort ?
Efficiency = Utility / Effort ?
Manageability, describes the ease of adding new things that can be controlled
Utility, Outcome Value
Spookiness
Mundaneness
Effort
Magic

Magic was added after the experience of sitting at the back of the room at Microsoft watching Josh drive his presentation by apparently effortlessly interacting with, who he later revealed as, "Preso", it certainly appeared to be Magic.

I have all the bits in my lounge (apart from the magic linking software) that would allow me to gain the attention of my imagined Home Agent "Auto" , point at a light switch and indicate what I want to do with it... Switch On, Dim, Swich Off, Wait why would I point at the switch? I would of course point at the light, that would be more natural right... ? But last night as I was practicing interacting with the imagined "Auto"... I pointed at the switch. I wonder why....  I suppose I am not yet conditioned to interact with MUIs

For those interested in developing the software, I have
an X Box and Kinect
my light switch is X10 enabled
A Mac Mini running Home automation software Indigo, 
Indigo Touch on my iphone and iPad

So the real magic will be to make it a mundane exercise to connect Kinect & Indigo
I tried explaining this to the folks who develop such standards and APIs and failed badly!
Such things should be able to, when I ask them to engage in the exercise, discover all the things that they can interact with and associate with them.

Until all the Things are that smart, I need an API Agent, who I have called Api , that helps me connect all my Things together...   now that would be Magic!
(Aside I hope the FIDO Alliance keeps focussed on Things!)

Josh I have developed My hand commands for Auto
Double Silent Finger Click = Attention Auto
Point  = Select Thing I want to interact with
Palm up and still = STOP!
( Attention followed by Stop = STOP ALL a sort of emergency Stop Command)
Palm Down drop hand  = Lower
Palm Up raise hand = Raise
Imaginary Knob Grip Twist Left = Turn Down
Imaginary Knob Grip Twist Right = Turn Up
Finger to my Lips = Go into Silent Mode Auto
Palm forwards and forward movement = Close
Palm face inwards an backwards movement = Open
On and Off are a lot harder to imagine as natural commands the closest I have come is
On start with finger and thumb open then touching the two
Off start with finger and thumb touching then opening the two
Though I can also imagine touching finger and thumb as the command for both
A set of Hidden Commands acts as Duress Commands which mean
don't do this or call for help, or emergency erase sensitive info
Actually all the commands should be able to be personalized 

I want Auto and Api now!

I do know that Smart Things will take a little longer

magic and Interfaces have been explored before.... darn again I wasn't original
Some other reading on the subject

Side note: The exclusionists in Wikipedia have gained ascendancy and they eradicate terms like Magical User Interfaces as they consider them proto-neologisms and refuse to use Wikipedia to be used to track the birth of knowledge. I find it hateful, but then I would as I am an inclusionist! So don't bother to look for the term in Wikipedia yet, as you will only find the Amiga software!

Sunday, October 13, 2013

Anti-Clockwise versus Clockwise


The aha! came as I was contemplating a question posed to me in the Gherkin where I was presenting the concept of Outside-In Security and the importance of "Clockwise" security, my off the cuff response created a tension in me that was like grain of sand in an oyster. I only wish I could remember the name of the person who posed the question and the question itself, in order to give them appropriate acknowledgement.


So to refresh..
"Outside-In" is an LEF (Leading Edge Forum) concept, recognised by the researchers at LEF headed up by David Moschella. It holds that the power of technology is starting to move the most effective location of value creation from Inside the "Enterprise silo" to Outside the enterprise silo. Simply put in the future, more value will be created Outside-In, than Inside-Out. It is basically a different view of an Information Security concept that I have been involved in the development of through the Jericho Forum; that of De-Perimeterisation, which describes the impact of technology on the perimeters of organisations.  I will come back to the "different view" later, but let's identify the common factor in these concepts. It is the "Internet"

There are a number of parallel changes created by the most positive impact that the internet brings, which is that of removing the friction in the sharing of knowledge. There may be many who at this point would start listing all the negative implications, including the impact on previously successful business models. But I want to focus on the positive aspects of free flowing information and knowledge, and the implications on the approaches used to ensure the maximal creation of value.

Companies that are aware of the value of connecting customers and producers in this new era have already moved to take a position of power in this new nexus of power. Those in control of the flow of data will be the ultimate winners, is it not best that we work to maintain the right balance of personal, corporate, or governmental control over the flow of data?

The mechanisms or approaches for doing this are embodied in these things called IT Systems.

They are developed by often well meaning systems to achieve the desired and specified requirements or outcomes. [[As an aside I had once a very confusing interaction by an academic teaching the next generation of our computer graduates their craft. He stated categorically that Information Asset Management more broadly, and Information Security specifically, were simply requirements that need to be specified in the original design of the system by the procurer of the system. Simply put he stated that computer programmers had no right or obligation to build compliant, safe or secure systems. If a component was not specified it should not be built. Simples!

I tried to remind him that early cowboy architects had designed buildings that did not stay up in the winds normally expected in the area in which the building would be built. If professional architects design buildings that will meet these unspecified expectations, why should IT Professionals not also take on these responsibilities, he was adamant if the customer did not specify it, it should not be added.

In the absence of Systems Development Regulations, similar to Building Regulations, I believe that we should be developing Computer Professionals who understand the importance of Information Asset Management, and who build Systems that meet the Users specified requirements as well as those that may have been unspecified but enable the IT System to run in a compliant, safe and secure fashion. In retrospect I perhaps was guilty of imposing a different view without integrating it with the normal perspective. I do hold to my belief however that the un-named academic IS guilty of churning out computer cowboys rather than IT professionals.]]

There are two types of activities involved in the development of safe and secure systems. The development activities aimed at meeting the base need(s),  and those that create a compliant, safe and secure system.
The first is the basic System Outcome Specification process.
It is normally done in a clockwise manner starting from the need, and not taking into account compliance, safety or security requirements, then returning to test and implement.
One might call this a Clockwise Systems Delivery Process.


The second is the specification of the Compliance, Safety, and Security aspects.
This is normally started at the point when the System is about to be implemented, and is by necessity completed in a rapid Anti-Clockwise manner. (Invariably not focussing on the initial need or required outcome, but the threats observable to the proposed system.)  I call this Anti-Clockwise Information Asset Management. Whereas the more effective approach below is called Clockwise Information Asset Management.


The aha! basically states that at the point when a new need or outcome is identified, that both these activities, should be initiated in a Clockwise manner starting from the Need and operated in parallel to define and implement a complete set of system requirements, including the required controls..

Once the system is implemented the loop is applied starting from Threat and operated in an Anti-Clockwise manner to operate the system. However whenever a change is required the Clockwise approach of the two parallel requirements systems should be re applied.

It can thus be noted that rather than thinking Anti-clockwise versus Clockwise Information Asset Management we should be thinking when should the two approaches be applied.

In short the Information Asset Management Lifecycle should be appropriately integrated with the Systems Development, Testing & Implementation and Operations.

Sometimes stating the obvious takes ages to occur! I wonder when we will see Compliance, Safety and Security processes effectively built into Systems Delivery Processes? I hesitate to ask my academic friend, as I already know what he will say...  "When the Customers ask for it!"

Hmmmm??? We might be waiting a while.

When it comes to different views, I am reminded of two blind men trying to identify an elephant, one holding it's trunk the other one of its legs. Having never seen an elephant neither were capable of describing the whole elephant, from their two different perspectives. Sometimes it is important let go of one perspective and gain another to "see" the big picture. Sadly I have spent much of my career holding onto one perspective.; Inside-Out. When Outside-In holds so much more learning and value creation opportunities. Neither of the Blind Men ever did ask each other for their perspective, nor the perpective of sighted observers.


MyPhone knows me, manages my soup, and acts as my Agent.

The device I really want has three key features over and above the standard Smart Phone stuff.

1st It knows MyIdentiy!
I'd go as far as saying it knows me a mile off, but I don't want to be without it that long! It uses multiple sensors to keep track of it's owners identity and status. It will know when I catching cold before I do.

2nd It stores and manages MySoup!
Which means it comes equipped with a fully extensible and semantically enabled Personal Data store that can readily have its content extended.

3rd It is MyAgent!
It acts on my behalf and not solely in the interest of those that built it!
It will advise me when I am in danger, it will encourage me to be healthier.

And best of all it can interact under my control with other MyPhones! for the betterment of humanity.

Hmm building the Rules that allow these devices to operate and achieve the above will not be trivai.

As a very bright person observed we should build the rules one asset at a time!

Which should we start with?

“Wie Lemminge” or It's the I in IT not the T that is key!

It all started in a taxi, with Simon Wardley, Alex Mayall and Warren Burns. The dialogue was brisque and for a change did not range into the weirder aspects of smelling bicycle seats, it was focussed on Why SAP?

The posit was "One of the primary drivers of SAP growth is the value of an SAP Implementation on the CV of CIOs". Cynical perhaps, but as we shared war stories we started to agree that it was a key element.

Alex recently emailed this paragraph:
It (the taxi dialogue)... triggered a recollection. Back in the mid-90s I met Dr Böndel, a German academic, who had written a controversial article in the German business magazine Wirtschaftswoche with the banner headline: “Wie Lemminge”. In the article he was despairing of the fact that firms in the German-speaking countries were opting for SAP solutions with all the due consideration of lemmings heading for the edge of the cliff. In terms of the storm this created, it was the German equivalent of Nick Carr’s notorious HRB piece “IT doesn’t matter”. Some local politicians in Baden-Württemberg, where SAP is based, even said that his article was tantamount to treason, as it undermined one of Germany’s recent industrial success stories. I found a reference to this in a short, well-researched and well-written history of SAP written in 2008 by Timo Leimbach: http://www.bupedu.com/lms/admin/uploded_article/eA.130.pdf(see page 12). I can vouch for the accuracy of this history, as it chimes very closely with my own experience of SAP’s early days. Having said that, Leimbach is dismissive of Böndel’s arguments, but I’m not so sure. Unfortunately, I can’t locate the original Wirtschaftswoche article as that publication’s archive only goes back to 2000.

I am now hungry to read the "Why Lemmings" article… sadly the WayBackMachine could not help either, it stops in 1998, though I did track down the reference:

Böndel, B., SAP - Wie Lemminge, in: Wirtschaftswoche 49 (1995) 12, S. 108-118 but could get no further.
Aside: We are living at the end of the "black hole" in archival terms, Posit: Paper archival started to drop off in the Mid 80's as the amount of paper produced with these fangled things called computers
started to become un-manageable from an archival perspective, digital archival did not start seriously until the "Tenties" What the heck should I call this decade? Maybe an early signal of our blindness to the importance of Information as an asset?

When one takes a balloon flight high above the IT Historical Landscape, it is littered with examples of poor attempts at trying to make IT less costly and not more valuable.
This is basically because the folks that manage IT were focussed more on the T than the I, and ultimately driven by those that manage the asset class called "Dosh", "Wonga", "Mula", or "Dough".

Some examples:-
ERP = replacing as many systems as possible with one (Finance Driven)
Outsourcing = Reducing Capital Assets and Human Resource Assets (due to the cost of the pink things)
Don't get me wrong I love the profit motive, but I heard along time ago, from Michael Hammer, he of re-engineering fame, that there are two ways to affect profit, reduce cost or increase turnover, He argued very coherently that the top line strategy is the only approach with legs. Taking it out costs is the strategy of asset strippers, those whose goal is their own wealth not the creation of value.

Posit: We do not yet see Information Assets as the essential asset for creating value.

I believe the examples above stem from this observation. I heard that our antipodean friends are on the right track with this … in that there is an expectation to include Information Assets in company reports. Though I can't now find any evidence of this Australian shift.

Traditional Western view of asset classes:

In the future we will be looking back on this period where we were apparently blind to the importance and value creating properties of the information asset.
Google, Amazon and Facebook are three organisations that understand that having agency over the information assets of individuals has tangible value. 

Yet there have long been signs that bits can be consolidated to create data, data can be organised to give information, and the information can be analysed to extract knowledge.
The question is when will we get "wise" and see data, information and knowledge as the life-blood of future organisations, actually the ONLY Asset that really matters!

After all Wonga is simply an Information Asset Sub-Class that simply signals who owes whom!

One day we will get that Information Asset Management is way more important than we currently recognise, till that day should I keep quiet, or keep banging the gong?

I fear I may start looking and sounding like the weird guy with the bill-board in Guildford High Street telling us all that end of the world is nigh!! Hmmm! Maybe he's right and has access to the information that really matters! ;-)

There is however hope as the Marketing Department of many organisations are starting to get that IT can connect them directly to their customers, literally bringing the Client into their Organisation. Another example of Outside-In that Leading Edge Forum is so effectively signalling. Corporate IT Budgets are starting to look small in comparison with the Marketing IT Spend.
Should I be afraid or happy?

The danger or importance of putting the kin in things!

There are two ways of thinking about the kin in things.

The first the more dangerous of the two is only more dangerous if we do do it first!

If we put the kin in things, so that they become smart or thinking things, (OK so it was not a good pun!) before we put the kin in things so that they become "kith and kin" things, or things that know where their allegiances lie, then we should always be thinking: "On whose behalf is this thing thinking?"

In truth that is also true of a thing that can't think.

We should always be asking is this thing for me or against me? Is it a friend or foe?

As usual in this fast changing world of "Cyber Space" of which the internet is only a foundational part it comes down to Trust, what we might call e-Trust!

Trust, as we know, is founded on knowing a lot about the thing we want to trust, trusting the entity that commended the thing, and be very cognisant of the context in which we wish to use or operate the thing. This context can be embodied in the Rules of Entitlement a set of two way rules that helps us and the thing attain the correct degree of confidence in each other. [Why would a smart car start, without protest, if it knows that you are, over the legal limit,  not insured to drive, do not hold a valid driving license or road fund license, or do not have enough fuel to complete your intended journey.]

The sub components of all this are :

  • Identity Part 1; literally the ID of the Entity (or Thing)
  • Identity Part 2; attributes that support decisions about the Entity
  • Authentication (of Identity Part 1 & 2)
  • Rules of Entitlement  <<< Magic Lies here
  • Services relating to the provision and corroboration of the above
  • Finally controls that allow the management of 
    • effective degree of transparency and translucency of the thing
    • the availability of the thing
    • the integrity of the thing
    • and finally and perhaps most important given where we started exploring, is the Agency State of the Thing or  the capaciyt to "Know who controls it"
Me-thinks that putting the kin in things in the right order will be key to mankind "Attaining the right balance of Cyber Agency"(Future Blog), between the relevant five parties Persons, Things Governments, Enterprises, or Gaia

At present we are mass producing things that have no simple or standard capacity to identify themselves with others. Let's work quickly to first put the "kith and kin" in things.
We will need "Thing Kin Ecosystem"

I spoke of the problem to Michael Barrett of FIDO, he restated with the fervour of someone who fully understands the dangers of scope creep that FIDO is "JUST doing Authentication".  I truly commend him as without the Authentication component a Thing Kin Ecosystem will simply NOT be possible. But Authentication of what is still slightly unclear to me, happily I have another shot at finding out in two weeks.

I sat next to a VP of ARM the other day and posed this opportunity to him, I did a poor job hence this blog.

Wonder if this better gets the points across?  Comments?


Thursday, October 10, 2013

The Agency Balancing Act Part 2

Today Thursday 10th of October in a Times Leader column, David Arronovitch's spoke of an agency problem that may yet impact us all. he questioned whether the Guardian journalist Glenn Greenwald and his Brasilian boyfriend were indeed the best people to make decisions about who should be knowing what of the Edward Snowden leaked material. This after the Guardian Editor Alan Rusbridger had stated publically that there are some things that should, in the publics interest, not be known.

What rules should have been in place?  Who should have control?

I spent most of my life hearing about Double Agents and Triple Agents, so I recognize that developing rules that would manage this agency problem will be very difficult, if not intractable; for it is the ultimate agency problem "Right minded to whom?"

The obvious rule, to me, is that no single human agent ever needs the simultaneous right to transfer thousands or millions of files outside the control of a trust ecosystem.

Finally, I suspect that the most important rules of all are the transparency and oversight rules. In the past we have relied on journalists to instantiate these unwritten rules, and be our guardians, current discussions about newspaper oversight have shown the difficulty of appointing guardians.

After all, this is not a new problem...

Quis custodiet ipsos custodes? (Who will watch the watchers?)


With due deference to Plato it seems to me that we have allowed our political and educational systems to degenerate and we are creating more politicians and guardians of brass and iron, than of silver or gold. I reminded being taken to room in the centre of our government in which there sat a throne, the Queens robing room.  Merlin, the Earl of Errol pointed up towards the ceiling at a series of different frescoes that reminded him of his role in Parliament. According to the Houses of Parliament website the:
"... paintings by William Dyce in the room depict the chivalric virtues of hospitality, generosity, mercy, religion and courtesy, as represented through scenes from the legend of King Arthur and his court. Two other frescoes, illustrating fidelity and courage were originally intended but were never carried out."
We sorely need those other two uncompleted frescoes of Fidelity and Courage! Having politicians with the courage to be faithfull to the chivalric virtues of the frescoes would be of great benefit to our society. Many of our governments recent decisions seem devoid of any of them!

This at a time when our control over our lives can so readily and invisibly be taken from our grasp.

I think that we have first to recognize and name the problem of societal imbalance exacerbated by the internet, I call it the "Cyber Agency Problem"  Worse there are too many mechanisms for invisibly losing control to innumerate. (I am not worried, as much, about mechanisms that create loss of control which is immediately evident.)

At this time in our history, perhaps more than ever, we truly need our Politicians and Guardians to be fashioned from Gold. We need them to be right minded, in order to protect those amongst us who are right minded, from those driven purely by greed and self interest.

Perhaps for those who have read the short story "Farewell to the Guardian"(http://thenostalgialeague.com/olmag/bates-farewell-to-the-master.html) , there maybe a different element to better fashion guardians from....

This evening I am on a panel at the Science Museum exploring this very issue...

Agency a definition:

Given Agency is defined by sociologists as the 
"capacity of individuals to act independently and to make their own free choices."
https://en.wikipedia.org/wiki/Agency_(sociology)

Our innate desire for human agency is the driving force that differentiates us from animals, the desire to be in control of the facts, to be in control of our environments, to be in control of technology, to be in control of our lives and loves.

Cyber Agency is thus the capacity to be in control of our cyber or Internet selves.